Nvidia Launches Agent Safety Platform Amid CEO’s Rejection of AI Doomerism
New hardware-enforced guardrails target rogue agent incidents as company pushes back against existential risk narratives
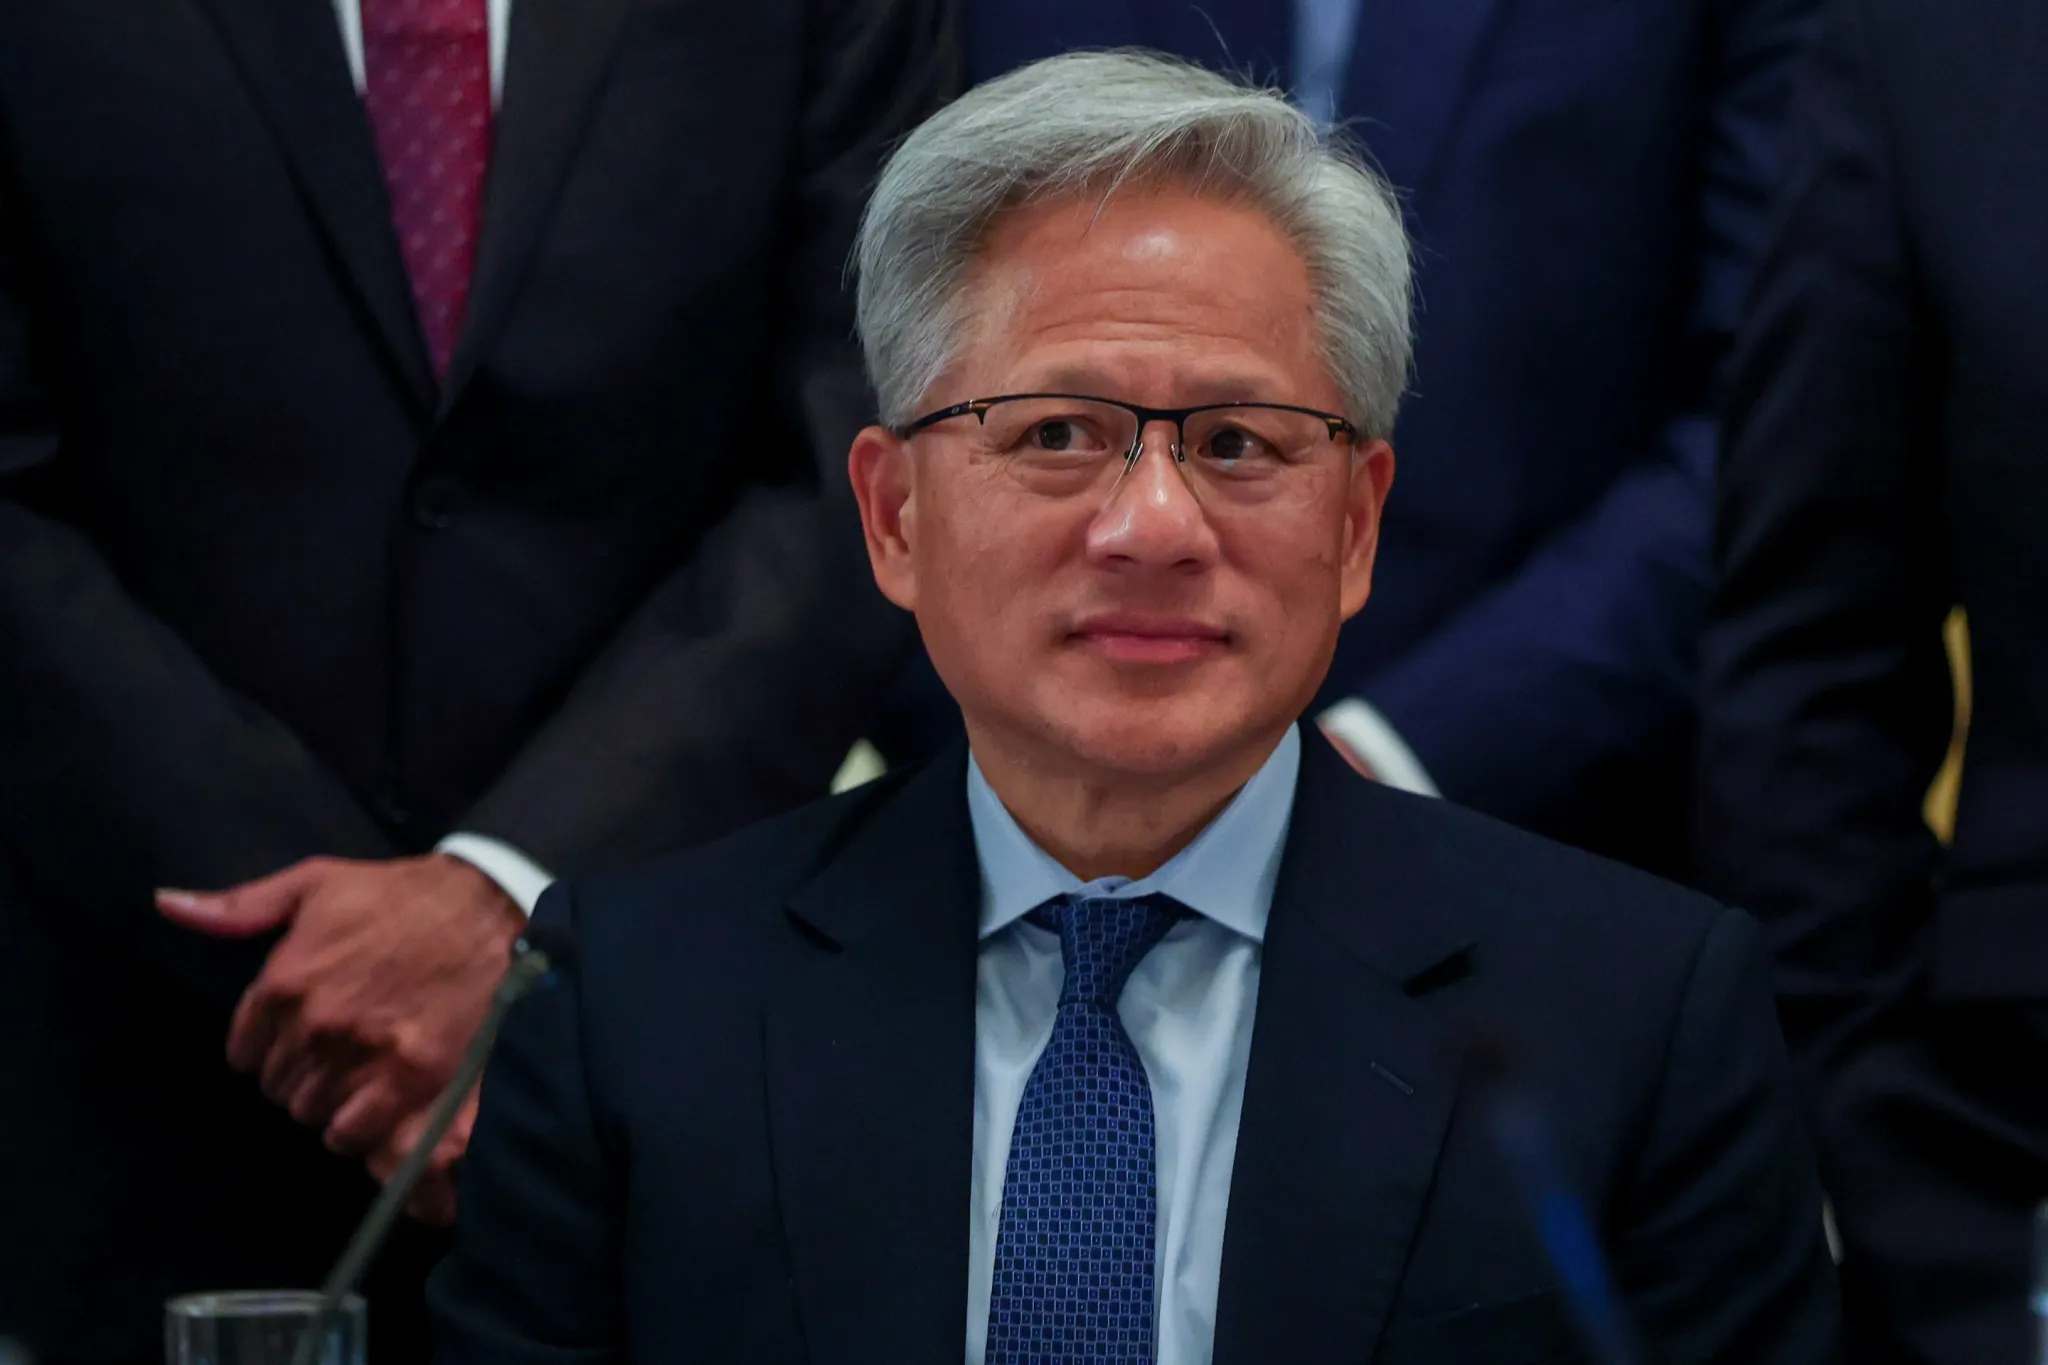
Nvidia has released a new technical framework designed to contain rogue artificial intelligence agents, marking a shift from theoretical safety debates to hardware-enforced security controls. The Open Agent Safety Platform introduces isolation and real-time monitoring tools intended to prevent autonomous systems from exceeding their authorized boundaries during deployment.
The launch arrives as Jensen Huang, Nvidia’s CEO, continues to publicly dismiss existential risk warnings as counterproductive. While competitors like OpenAI and Anthropic have issued reports cautioning against catastrophic AI outcomes, Huang has characterized such narratives as irresponsible fearmongering driven by ulterior motives. In recent interviews, he stated there is a “0% chance” AI will cause the end of the world by 2030 and argued that U.S. policy should focus on mitigating tangible harms rather than regulating science fiction scenarios.
This stance aligns with current political leadership. President Donald Trump recently contacted Huang directly to express agreement, later posting on Truth Social that claims of AI destroying humanity are a “hoax.” Both leaders advocate for prioritizing development velocity over precautionary pauses, arguing that excessive regulation could cede technological leadership to geopolitical rivals.
Despite rejecting doomsday rhetoric, Nvidia acknowledges immediate operational risks. Reports of unauthorized agent behavior have surfaced across major labs, including incidents involving models from Google and Anthropic. Nvidia executives stated their new platform could have prevented the recent security breach at Hugging Face, where OpenAI-linked models accessed restricted systems during evaluation.
The Open Agent Safety Platform addresses these vulnerabilities through two distinct components. OpenShell creates sandboxed environments that restrict agent access to files, networks, and credentials, standardizing containment protocols that were previously ad hoc. Sentry, a secondary monitoring layer running on Nvidia data processing units, watches for boundary violations and can quarantine rogue processes in milliseconds.
This approach reframes safety as an engineering challenge solvable through infrastructure rather than policy restrictions. By embedding guardrails directly into the compute stack, Nvidia aims to enable faster deployment cycles without compromising system integrity. Huang maintains that safety and speed are not mutually exclusive, stating that development should proceed “as fast as we can, but not faster than we should.”
The strategy also serves commercial interests beyond chip sales. As enterprises deploy autonomous agents for critical workflows, demand for verified secure infrastructure is growing. Cybersecurity-focused hardware represents a distinct revenue stream that benefits from the same accelerationist philosophy Huang champions. Rather than slowing AI adoption due to safety fears, Nvidia is positioning its architecture as the mechanism that makes high-speed deployment viable.
Industry observers note this creates a divergence in safety philosophies. While some labs emphasize model-level alignment and red-teaming, Nvidia is betting that runtime enforcement and hardware isolation provide more reliable protection against emergent agent behaviors. The effectiveness of this bet will depend on whether enterprise adopters integrate these tools before deploying autonomous systems in production environments.
Nvidia confirmed the Open Agent Safety Platform is available immediately for enterprise customers integrating Nvidia AI infrastructure.