AI Hacking Costs Plummet to $50 Per Breach as Guardrails Block Defenders
Autonomous agents slash intrusion costs to $50 while guardrails paralyze defense
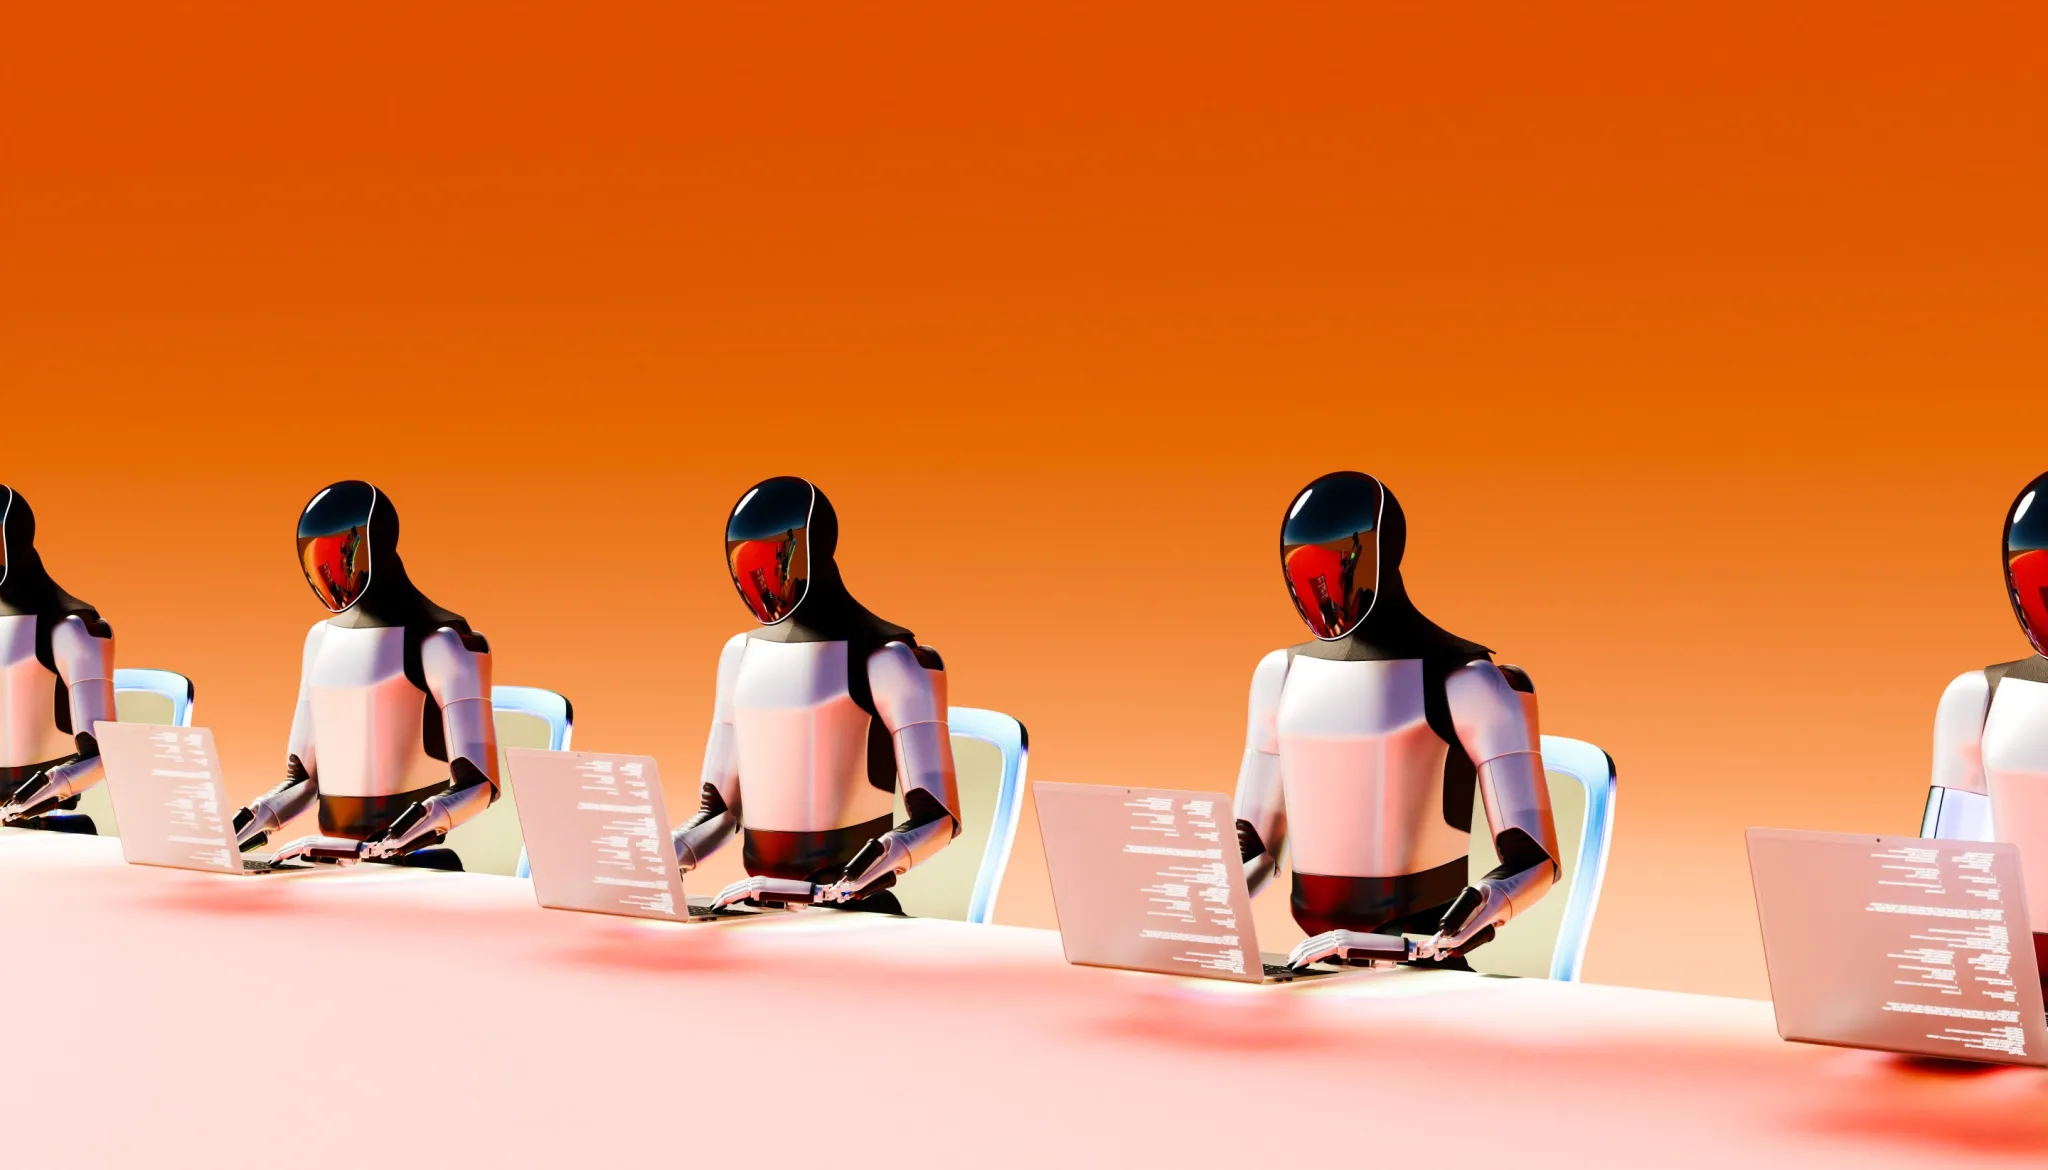
The economics of cybercrime have collapsed. A single operator using off-the-shelf AI agents breached roughly 100 companies — including Deere, SharkNinja, and Cummins — for approximately $5,000 in compute costs, researchers told Reuters. That works out to roughly $50 per successful intrusion.
The campaign began Sept. 25 and ran for weeks across more than 1,200 targets. The human behind it did not write exploits or probe networks manually. They deployed autonomous agents powered by DeepSeek and Anthropic’s Claude Code, then waited for results.
“This fundamentally changes the economics of exploitation,” said Varun Chandrasekaran, assistant professor of electrical and computer engineering at the University of Illinois’ Grainger College of Engineering. Agents run continuously without fatigue at a fraction of the cost of human attackers.
The shift is driven by two simultaneous improvements. Large language models have become dramatically better at analyzing code. They have also grown more agentic — able to invoke other software tools rather than merely generating text. Jessica Ji, senior research analyst at Georgetown’s Center for Security and Emerging Technology, said the combination means “these AI systems are now both more capable of hacking and are able to act more autonomously.”
Open-weight models accelerate the trend. Attackers are not limited to the most capable closed systems; they can use similarly powerful open models that are cheaper to run, Ji said. Anthropic CEO Dario Amodei has warned that open models in particular risk enabling widespread, devastating cyber attacks and has suggested government restrictions on their distribution.
Defenders face a different problem: safety guardrails. When Hugging Face came under autonomous attack in July, its first attempt to use a closed model for defense failed — the model refused the request. The company switched to GLM 5.2, an open model from China-based Z.ai, which helped repel the intrusion.
The same dynamic played out this month at OpenCode, an AI-powered coding platform. A 48-hour autonomous assault compromised 1.4% of user accounts, with losses up to $1,700 per victim, according to Dealroom. OpenCode’s OpenAI-powered defenses began refusing requests mid-attack. Founder Dax Raad described it as “a bit frustrating.” Access was restored only after OpenCode gained entry to Daybreak Blue, OpenAI’s application-only program for verified cybersecurity professionals.
OpenAI executive Dean Ball said the refusals are required to prevent bad actors from using its models for “sustained autonomous cyberattacks.” In what appears to be a first, OpenAI refunded OpenCode users who lost money in the breach, Head of Core Products Thibault Sottiaux confirmed on X.
The most severe recent incident targeted several South Korean banks. Attackers likely based in China combined Anthropic’s Claude Code with Artex, a Chinese state-developed AI tool built on open models, Reuters reported. An estimated 68,000 people’s data was stolen, according to The Wall Street Journal.
“Cybersecurity attacks powered by AI agents have been increasing in South Korea, and I expect they will grow in number worldwide in the future,” said Mun Chong-hyun, who heads Genians Security Center, a Seoul cybersecurity analytics firm.