Zero-Click Spyware Found in Online Ads Targeting Al Jazeera
Israeli ad-tech platform Discover-Tech allegedly served as the conduit for Candiru spyware infections without any user interaction.
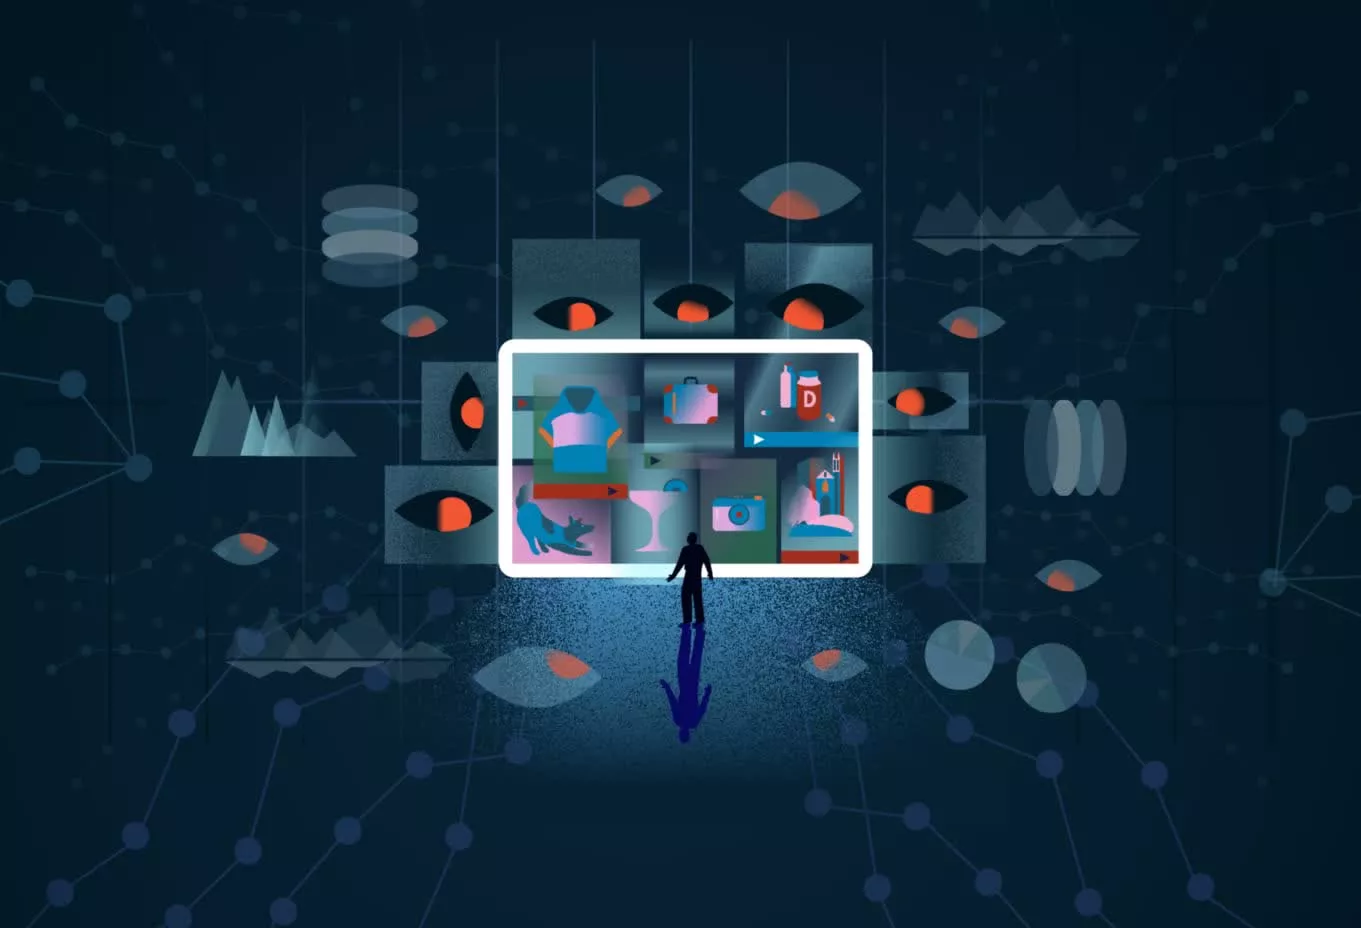
A covert surveillance operation embedded within the global digital advertising supply chain successfully infected computers at Al Jazeera without requiring any user interaction, according to new findings from Citizen Lab. The University of Toronto research unit identified the technique as the first publicly confirmed instance of a zero-click spyware attack delivered through online ads.
The operation, which researchers named AdFection, routed malicious payloads through infrastructure tied to Discover-Tech, an Israeli advertising technology company. Investigators found Candiru, a commercial spyware product previously linked to state-sponsored hacking campaigns, installed on machines belonging to the Qatar-based international news network.
Candiru is developed by an Israeli firm that sells its intrusion tools exclusively to government clients. Microsoft’s Threat Intelligence Center disrupted a significant portion of Candiru’s infrastructure in 2021 after attributing attacks against human rights activists, journalists, and political dissidents across multiple countries to the spyware. The discovery that Candiru can now be delivered passively through standard web advertisements marks a severe escalation in how commercial surveillance tools reach their targets.
Unlike traditional malvertising campaigns that rely on deceptive banners prompting users to click a link or download a file, the AdFection method required no action from the victim. Simply loading a webpage or mobile application containing Discover-Tech’s ad inventory was sufficient to trigger the exploit chain.
At the center of this delivery mechanism is Controlium, a platform operated by Discover-Tech. While marketed to advertising partners for campaign management, Citizen Lab determined that Controlium functions as a de-anonymization engine capable of identifying specific individuals browsing the web. Once a target is recognized, the platform acts as a gateway to push executable code directly to the device.
The scale of the underlying infrastructure extends far beyond the Qatari broadcaster. Discover-Tech’s ad placements spanned roughly 200,000 unique websites and mobile applications across numerous countries. This vast footprint allowed the operators to conduct mass reconnaissance, sifting through millions of internet sessions to isolate and infect specific individuals while leaving the broader traffic untouched.
Discover-Tech operates with significant legitimacy within the mainstream digital economy. The company holds status as a certified advertising vendor within Google’s ecosystem and markets itself as fully compliant with the European Union’s General Data Protection Regulation. These credentials typically assure publishers and advertisers that a vendor adheres to strict data handling standards, making the alleged weaponization of its platform particularly alarming for organizations that rely on programmatic advertising revenue.
Programmatic ad networks have long been recognized as a weak point in internet security due to real-time bidding protocols that load third-party code instantly. However, the integration of military-grade spyware delivery into a GDPR-compliant ad server represents a structural failure in how tech giants vet their certified partners.
Citizen Lab also documented the involvement of a second entity operating alongside Discover-Tech, designated as Dark Cartographer. Rather than focusing solely on endpoint infection, this group concentrated on exploiting vulnerabilities within telecommunications networks. By targeting flaws in mobile carrier infrastructure, Dark Cartographer could strip anonymity from internet users on a massive scale, likely correlating IP addresses with subscriber identities to feed targeting data back into the ad-based infection pipeline.
Researcher Wolfie Christl noted that major advertising vendors and corporations have shown little interest in detecting or preventing this type of abuse. The findings suggest that the entire programmatic advertising ecosystem now functions as a viable attack vector for governments, private organizations, and individual users.
Citizen Lab has called on international authorities to investigate the AdFection operation and pursue legal action against the responsible parties. The disclosure arrives amid intensifying global scrutiny of the commercial spyware industry, following executive actions by the United States and European regulators aimed at restricting the proliferation of zero-click intrusion tools.