

U.S. Sanctions Tren de Aragua Financial Network Behind $40 Million ATM Jackpotting Campaign
Federal prosecutors indicted 98 suspects while OFAC targeted the malware engineers and Mexican front companies moving stolen cash through crypto networks.

The U.S. Treasury Department sanctioned 10 individuals and entities linked to a Venezuelan gang’s cybercrime operation that drained more than $40 million from American bank machines, marking the first major financial strike against Tren de Aragua since its designation as a foreign terrorist organization.
The Office of Foreign Assets Control targeted the architects of an “ATM jackpotting” campaign that generated over 1,500 incidents nationwide through August 2025. The technique relies on custom malware installed directly into automated teller machines, overriding security protocols and forcing cash dispensers to empty their vaults on command. Federal investigators traced $40.73 million in reported losses from these attacks, with proceeds laundered through cryptocurrency networks before reaching cartel leadership operating across South America and Mexico.


Tren de Aragua, originally formed by inmates at the Tocorón prison in Aragua state, Venezuela, has expanded rapidly beyond its origins as a prison gang into a transnational criminal enterprise. The group established footholds in Colombia, Peru, Chile, and eventually the United States, diversifying from extortion into human smuggling, drug trafficking, and murder-for-hire. President Donald Trump designated the organization as a Foreign Terrorist Organization in February 2025, a classification that triggered broader sanctions authorities previously reserved for groups like Hezbollah or MS-13 under similar designations.
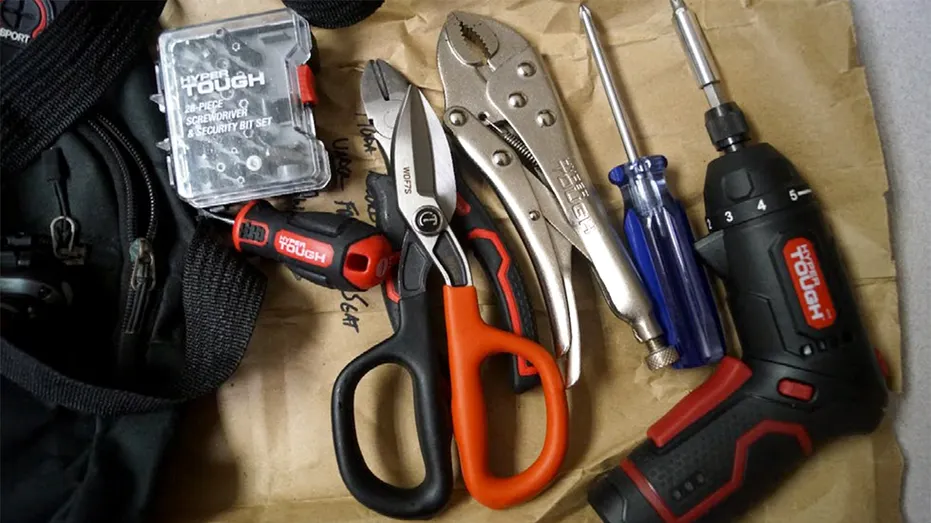
ATM jackpotting differs fundamentally from traditional card skimming, which captures magnetic stripe data or PINs to clone cards. Jackpotting attacks the machine’s internal computer, often requiring physical access to the terminal’s USB ports or network connections. Criminal crews typically use tools such as endoscopes, modified laptops, or direct wiring to inject malicious code—frequently variants of the Ploutus family of malware first identified in Eastern Europe over a decade ago. Once compromised, the machine behaves as though a legitimate withdrawal request is occurring repeatedly, bypassing account verification entirely. This distinction makes the crime closer to a bank burglary than electronic fraud, carrying heavier federal penalties.
At the center of the newly sanctioned network is Anibal Alexander Canelon Aguirre, known by the alias “Prometheus,” who remains on the FBI’s Ten Most Wanted Fugitives list. Operating between Mexico and Venezuela, Canelon Aguirre allegedly engineered the specific malware deployed by street-level crews across the United States. Alongside him, OFAC sanctioned Juan Gabriel Rivas Nunez, referred to as “Juancho,” a high-ranking facilitator managing the group’s gold-mining revenue streams—a parallel funding mechanism common among Venezuelan syndicates exploiting illegal mining in the Orinoco Mining Arc.

The sanctions also hit two Mexico-based front companies: Enigma Community, S. de R.L. de C.V. and Soluciones Integrales Toluca, S.A. de C.V. These corporate entities served as logistical nodes for moving illicit funds. Six additional associates—Carlos Javier Martinez Armenta, Alejandro Mejia Castillo, Jose Dario Galeano Bazurto, Eric Gabriel Cardenas Arzola, Oscar Leonardo Martinez Pirona, and Anthony Wuiliam Hernandez Guerrero—face federal charges including material support to a terrorist organization, bank fraud conspiracy, and money laundering via digital assets.
Since October 2025, the Department of Justice indicted 98 defendants connected to the cross-country jackpotting ring. The prosecutions rely on overlapping legal frameworks, combining Executive Order 13581, which targets transnational criminal organizations, with Executive Order 13224, the post-9/11 authority used to freeze terrorist assets. Applying both simultaneously reflects a shift in how Washington treats hybrid threats where organized crime and terrorism intersect.
Treasury Secretary Scott Bessent framed the action as a defense of domestic financial infrastructure. “President Trump’s administration will not allow terrorist organizations like Tren de Aragua to exploit the U.S. financial system or enrich themselves through theft and other criminal activity targeting American individuals and businesses,” Bessent said. State Department spokesperson Tommy Pigott issued a direct warning to enablers: “Under President Trump’s leadership, the United States is coming for you and your assets, no matter where you hide.”
The investigation was driven by the Homeland Security Task Force, coordinating the FBI, Homeland Security Investigations, the Financial Crimes Enforcement Network, and Joint Task Force Vulcan. FinCEN’s involvement underscores the role of anti-money laundering compliance in tracking the cryptocurrency conversions used to repatriate stolen cash. Banks and independent ATM deployers have increasingly faced pressure to implement hardware-level encryption and remote monitoring to detect unauthorized physical tampering, though older standalone terminals remain highly vulnerable to direct malware injection.
All 10 sanctioned targets now face blocked U.S. assets, and any American person or institution conducting transactions with them risks secondary sanctions. The 98 indicted individuals are currently navigating federal proceedings across multiple U.S. jurisdictions.





One Comment