Credit Mutuel Arkea Fell to the Same Playbook as Binance, One Week On
The bank says the attackers came through a supplier's platform and used its own account to move the money. An independent investigator spotted the theft on Monday; the bank confirmed it on Wednesday.
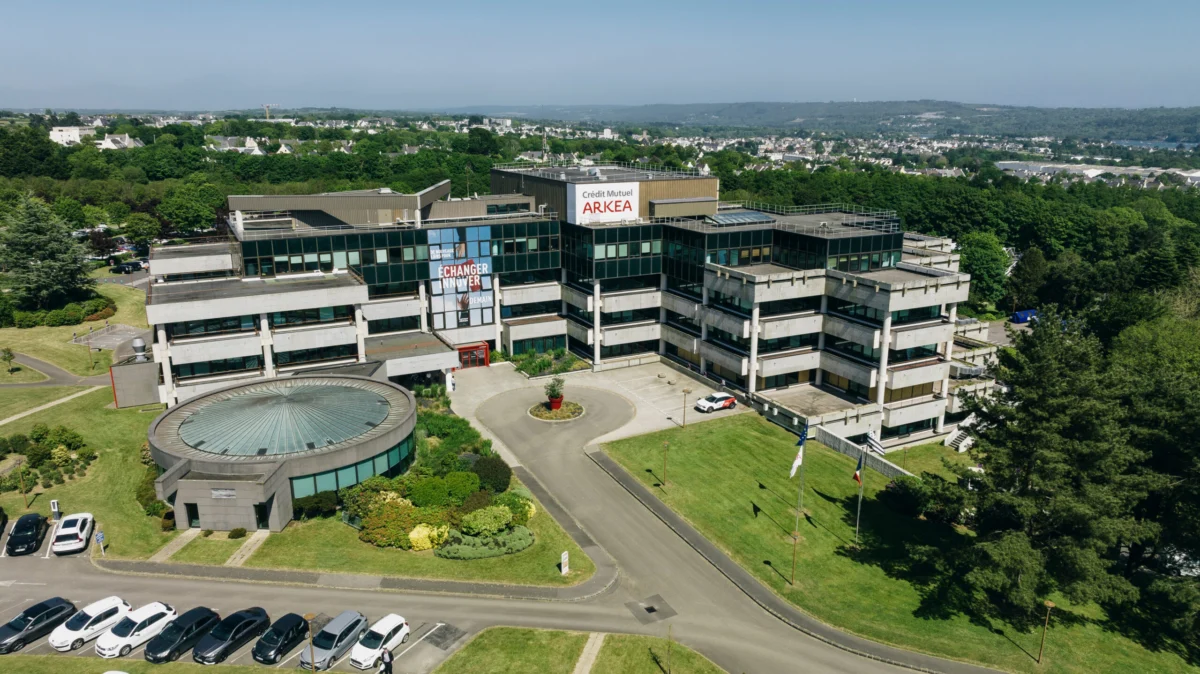
Kraken saw it first. On Monday, the American crypto exchange watched transfers from a European bank arrive too large and too fast to be ordinary, and blocked the ones still moving. The money had been leaving since Sunday, in stablecoins, through accounts at Kraken, Crypto.com and OKX. Two days later, on Wednesday, Credit Mutuel Arkea confirmed what a pseudonymous investigator had already named. Its own account had been used to send about €100 million out of the bank. The bank had not been the first to know. The investigator, ZachXBT, had put the theft at more than $133 million. The bank put it at about €100 million and would confirm only the order of magnitude.
The bank’s first estimate is about €100 million, and it told Reuters its losses were lower than the $133 million reported by CoinDesk. ZachXBT’s total is more than $133 million, or about €118 million, and he says it could grow once over-the-counter trades are counted. Bitquery, a blockchain analytics firm, traced $126.04 million in USDC withdrawn from the three exchanges to 17 wallets on November 1 and 2. The firm says of its own count against the other two: “We cannot yet explain either gap.” The bank, asked whether €118 million was stolen, said it does not confirm the figure and can only validate the order of magnitude. Part of the money has been blocked, the bank says, and recovery work is under way.
Binance published its own account of the first heist on Tuesday, November 3. The campaign began in June, when a wallet DevOps engineer the report calls Engineer A searched for a popular AI coding tool and installed it through a tampered Homebrew package. Binance caught the anomaly, replaced the laptop and rotated every credential tied to it. The attackers had learned the names of Engineer A’s team. In September, another software engineer was contacted through a legitimate job-hunting platform by someone posing as a project director. The fake company ran him through a live video interview with a fake HR representative. She shared a social media account with personal photos and videos to build trust. Then came a second interview with a fake chief executive on a popular social chat app, who told him to download an “assignment” containing a malware-laced code repository. On October 20, the attackers used the compromised computer and an internal AI tool to reach the computers of Engineer A and a wallet software engineer the report calls Engineer C. Engineer A had a container deployment permission token on his machine. On October 29, between 17:15 and 19:56 UTC, the attacker logged onto Engineer C’s computer with Engineer A’s credentials, deployed a container and ran a script that reached the exchange’s internal wallet signing service. From 20:05 UTC, about $6.3 billion left Binance’s hot wallets. The FBI attributed the theft to TraderTraitor, the North Korean operation tracked as the Lazarus Group. Binance paused withdrawals for about 45 hours and reopened them in phases on the morning of November 1. Six hours later, the first of the Arkea withdrawals left OKX.
The bank’s account of the Credit Mutuel Arkea hack came the next day, in a question-and-answer note. The attackers went through the platform of one of its service providers and reached the bank directly. They used the bank’s own account to send transactions to other banks, which may then have enabled them to convert the money into cryptocurrency through specialised platforms. They did not go through the accounts of customers of its federations or subsidiaries. The bank denied press reports that the attackers got in through Fortuneo, its online bank, and said the attack was a sophisticated one from outside, not the result of human error. Neither set of attackers broke into a vault. Both used access that already existed: a deployment token on an engineer’s laptop in one case, a service provider’s platform in the other.
Bitquery followed the Arkea money from the 11 addresses ZachXBT first posted, and counted $126.04 million withdrawn to 17 wallets over 28 hours. The first withdrawal left OKX at 12:25 UTC on Sunday, November 1. Kraken followed 44 minutes later and ended up paying 95 percent of the total, in 187 withdrawals. In the three hours to 23:00 UTC, $73.2 million left. By 23:10, 84 percent was gone. Overnight another $2.6 million went out, nearly all of it to one wallet. Then the payouts stopped. Six and a half hours later they started again: between 15:46 and 16:30 UTC on Monday, Kraken paid $17.2 million to two more wallets, in nine payments. That was after ZachXBT’s first post had gone up. The money did not sit still. The median wait before the USDC moved on to a fresh wallet was five minutes, and one wallet took 43 Kraken withdrawals in 91 minutes, each under $50,000. Within hours, half of it was ether. A fresh wallet sold $62.98 million of USDC and USDT for 27,553 ether through UniswapX in about four hours. Another branch swapped into DAI. It has no freeze button. The biggest single route out, $36.09 million, went through LI.FI, a bridge and swap router.
Twelve of the 17 wallets had taken payouts from the same exchanges before the theft. Two of them had been paid since May. Together they took 79 percent of the money. The oldest had taken its first Kraken withdrawal on May 4. It took 48 more before the theft. It paid the money on in round sums. Nine of the 17 are Trust Wallet smart accounts, set up to pay network fees in USDC, and so are 22 of the thief’s addresses. Bitquery’s reading is that the exchange accounts and the wallets belonged to the attackers from the start, and the earlier use was part of the setup. The bank’s side of the theft was bank transfers, so it leaves no trace on the chain.
Tether froze 1.14 million USDT at 23:10 UTC on Monday. It was the first freeze. The thief had swapped 500 ether into that USDT hours earlier. Four minutes before the freeze, he had sent 4,450 ether to the same wallet, which Tether cannot touch. Circle, the company behind USDC, froze none of the thief’s coins. At 08:47 UTC on Thursday, 1.71 million USDC was still in the thief’s hands. Bitquery noted that the swap ran for four hours with no freeze at all. “We do not know whether anyone asked Circle to act.” After the Binance hack, Tether and Circle froze more than $2 billion within hours. Here, three days after the theft, 5.16 million USDC was still within Circle’s reach. At the Thursday snapshot, $37.26 million still sat on Ethereum in addresses tied to the thief, mostly as ether, and $95.8 million had left. The bank informed the Banque de France, which houses the prudential supervisor.
On October 31, the FBI attributed the Binance theft to TraderTraitor, the North Korean operation tracked as the Lazarus Group, and North Korea denied it on November 3. ZachXBT, the investigator who spotted the Arkea money, said he has a high degree of confidence that the attacker is not associated with North Korea’s Lazarus Group. His reason is the way the stolen funds were moved. The Arkea thief swapped slowly, over days, into ether and DAI and Monero through instant exchanges, while Lazarus is known for moving fast through mixers. Le Monde’s experts offered two other hypotheses: drug-trafficking circles with staggering resources, for whom laundering money is a second business, and the possible complicity of a disgruntled employee. Gabriel de Brosses, a former head of cybersecurity at Groupe La Poste, said one thing was certain. The amount stolen and the stealth of the operation showed very detailed knowledge of banking procedures. The bank has not said when the attack began, who was behind it, or whether any data was taken.
On Reddit, in the French personal-finance forum r/vosfinances, the thread asking whether readers were customers of the bank or of Fortuneo drew 98 comments. One user, u/Areat, wrote in French. “C’est un peu la version moderne d’apprendre que sa banque s’est faite braquée.” (Translation: “It’s a bit the modern version of learning your bank got robbed”). Another, u/LaColleMouille, put the two heists in one sentence before the newspapers did. “Alors que le hack de Binance, heureusement que que les français se font pirater /s” (Translation: “Right after the Binance hack, lucky the French are getting hacked /s” — the /s marks sarcasm).
“Aucune raison de changer de banques, elles ont toutes les meme failles, de bourso a n26,” wrote u/Demethyl84. (Translation: “No reason to switch banks, they all have the same flaws, from Boursorama to N26”). The shrug answers the shock in Le Monde, where one banking cybersecurity veteran said, “I am stunned,” and Gabriel de Brosses said that normally this does not happen to banks. A Fortuneo customer, u/hakak34, reported what the bank’s “delay in certain transfers” looked like from his side. “Je sais pas si c’est lié mais j’ai un compte Fortuneo et depuis ce matin je n’arrive pas à y faire de virement instantané depuis un autre compte.” (Translation: “I don’t know if it’s related, but I have a Fortuneo account and since this morning I can’t make an instant transfer from another account”). “J’ai un message d’erreur disant que la banque destinataire, Fortuneo donc, n’accepte pas les virements instantanés.” (Translation: “I get an error message saying the destination bank, Fortuneo, doesn’t accept instant transfers”).
The Paris prosecutor’s office opened an inquiry on Wednesday, and France’s anti-cybercrime police are investigating. Credit Mutuel Arkea has not named the supplier whose platform the attackers used. Kraken, which paid 187 of the withdrawals, can say who opened the accounts and with what papers.