MediaMarkt Pulls Ledger Wallets Amid Tampering Probe
Supply chain investigation expands beyond CryptoBilis as European electronics retailer halts hardware wallet sales
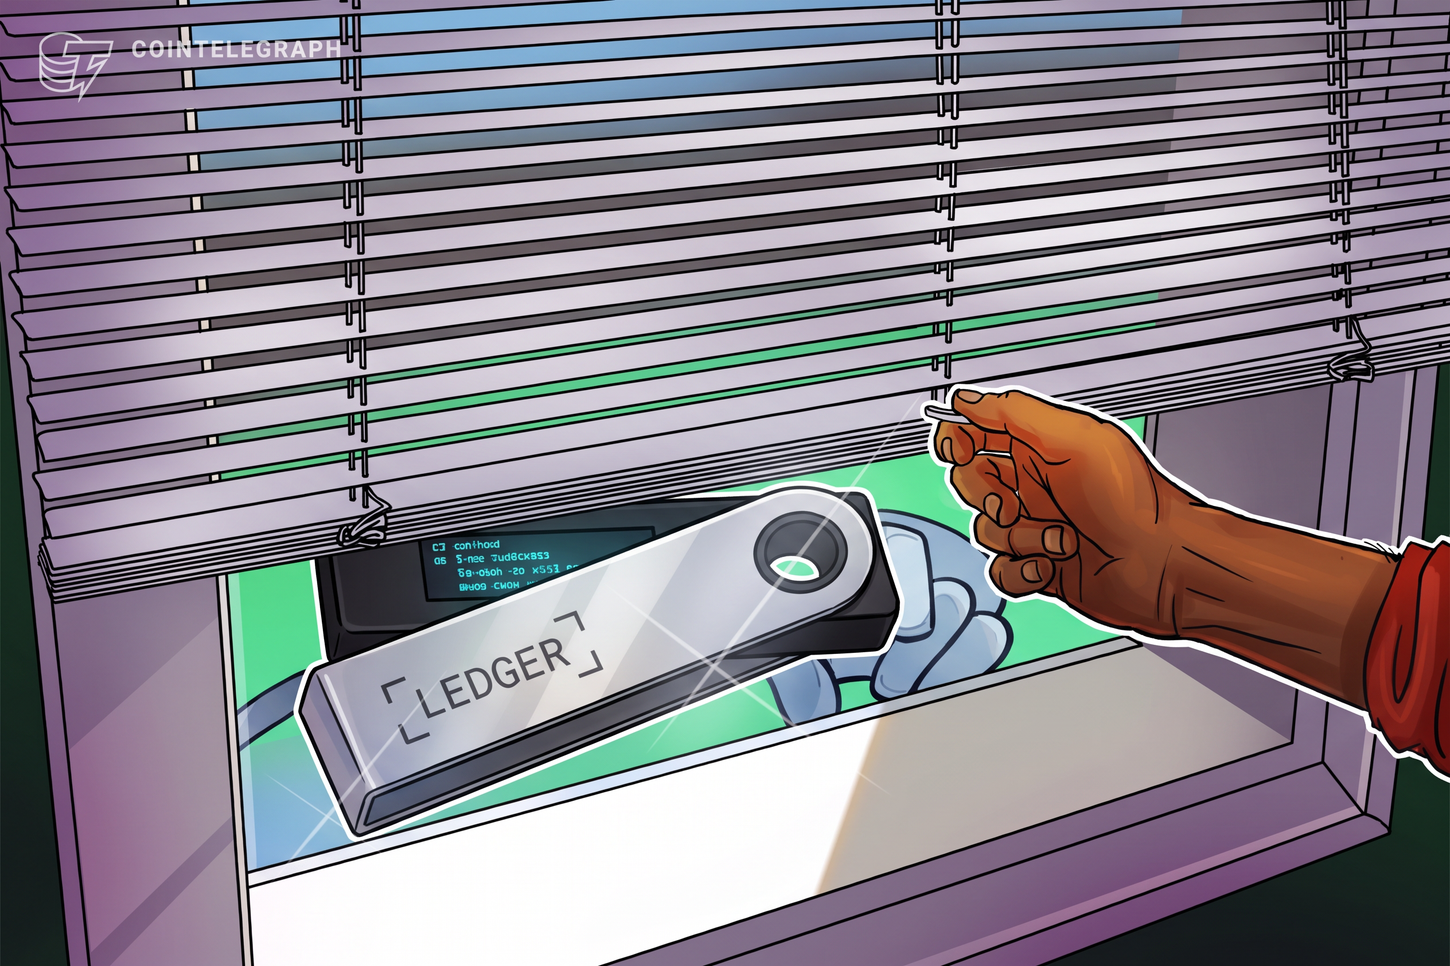
European electronics giant MediaMarkt has removed Ledger hardware wallets from its retail inventory as the cryptocurrency security company investigates reports of physical device tampering extending beyond previously known incidents.
The precautionary pull affects stores across multiple European markets where MediaMarkt operates. The retailer, one of the continent’s largest consumer electronics chains with hundreds of locations primarily in Germany, Spain, France, and the Netherlands, acted after Ledger disclosed that its internal probe into compromised devices had widened in scope.
Ledger initially identified tampering linked to CryptoBilis, a distributor operating in Southeast Asia. The company’s ongoing investigation has since uncovered evidence suggesting the supply chain interference is not confined to that single regional partner or geography. Specific details regarding which additional distribution channels or regions are affected remain under active review by Ledger’s security team.
Hardware wallets serve as cold storage for cryptocurrency private keys, keeping them isolated from internet-connected devices. Their entire security model depends on an unbroken chain of custody from manufacturer to end user. Any unauthorized physical access during shipping or retail handling can allow attackers to install modified firmware, swap internal components, or pre-configure seed phrases — effectively granting thieves control over deposited assets before the legitimate owner ever powers on the device.
This incident echoes a persistent vulnerability in the hardware wallet industry. In 2020, Ledger suffered a major data breach exposing approximately 270,000 customer records, which subsequently fueled targeted phishing campaigns and physical extortion attempts against users. That history makes retailers and consumers particularly sensitive to any new indications of supply chain compromise.
Physical tampering with hardware wallets remains relatively rare compared to software-based attacks like phishing or malware, but carries far higher financial consequences per incident. Unlike digital breaches, compromised physical devices often bypass standard security warnings because the hardware appears authentic and functions normally until funds are transferred.
Consumers who recently purchased Ledger devices through MediaMarkt or other authorized retailers are advised to verify packaging integrity. Standard verification includes checking holographic seals, confirming the device boots directly into Ledger’s official setup process rather than a pre-configured state, and ensuring no recovery phrase is included in the box. Ledger’s architecture requires users to generate their own 24-word seed phrase exclusively on the device during initial setup; any unit arriving with a pre-printed recovery phrase is definitively compromised.
Neither Ledger nor MediaMarkt has published a timeline for when products might return to shelves. The resumption of sales will depend entirely on the findings of Ledger’s expanded forensic investigation into its global distribution network.