

EU Financial Regulators Warn Quantum Computing Could Expose Stolen Data and $469 Billion in Bitcoin
Supervisors urge encryption audits as governments prepare post-quantum migration strategies.

BRUSSELS — European financial regulators have warned that encrypted data stolen today could be read in the future by state-sponsored actors and cybercriminals using quantum computers. Their warning extends from bank records and sovereign communications to public blockchains, where an estimated $469 billion in Bitcoin is held at addresses with visible public keys.
In a joint autumn risk assessment, the European Banking Authority (EBA), the European Insurance and Occupational Pensions Authority (EIOPA), and the European Securities and Markets Authority (ESMA) said an advanced quantum computer could undermine the mathematical foundations protecting bank transactions, corporate databases, sovereign communications, and blockchain networks. They warned that the ability to break encryption could emerge “earlier than any viable commercial application” of quantum technology.
Experts estimate that a quantum computer powerful enough to crack modern encryption standards is still years away. The regulators said the threat is nevertheless active: under a tactic known as “harvest now, decrypt later” (HNDL), adversaries are intercepting and archiving sensitive encrypted financial and governmental transmissions for future decryption. In the regulators’ assessment, intercepted financial or cryptographic data that will retain strategic, commercial, or sovereign value over the next decade is already compromised.
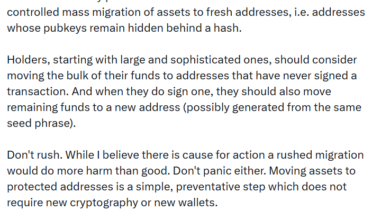
A nation-state or other hostile actor could develop a cryptanalytically useful quantum computer (CRQC) for breaking encryption before quantum technology delivers commercial benefits in medicine, logistics, or chemistry. Public blockchains face a particular exposure because their ledgers are transparent and some addresses reveal their public keys directly, allowing an attack without any new transaction by the owner.
Blockchain analytics firm Glassnode estimates that about 6.04 million Bitcoin, or 30.2% of the circulating supply, sits in addresses whose public keys are visible on the blockchain. At current market valuations, those holdings amount to hundreds of billions of dollars. The exposure chiefly concerns Pay-to-Public-Key (P2PK) addresses used in Bitcoin’s early days, along with addresses that have spent funds once but still hold a balance.
The warning comes as governments and financial institutions move toward post-quantum cryptography (PQC). In the United States, the National Institute of Standards and Technology (NIST) has finalized its first official encryption standards designed to withstand quantum attacks, including ML-KEM for general encryption and ML-DSA for digital signatures. They are intended to replace legacy public-key algorithms such as RSA and Elliptic Curve Cryptography (ECC), whose underlying mathematical problems could be solved almost instantly by quantum computers using Shor’s algorithm.
Modern Pay-to-Public-Key-Hash (P2PKH) blockchain addresses are mathematically safer because they conceal the public key behind a double hash, SHA-256 and RIPEMD-160, until a transaction begins, providing a layer of quantum-resistant protection. Industry estimates place “Q-Day” — when a quantum machine could break the Elliptic Curve Digital Signature Algorithm (ECDSA) underpinning Bitcoin and Ethereum — between 2030 and 2032. Some researchers say faster hardware scaling could bring that date significantly closer.
Within the European Union, the Digital Operational Resilience Act (DORA) requires financial institutions to maintain state-of-the-art cryptographic defenses against emerging cyber threats. The EU’s NIS (Network and Information Systems) Cooperation Group has separately recommended that member states put national post-quantum cryptography migration strategies in place by the end of 2026 to ensure synchronized systemic resilience.
The three supervisory authorities also described quantum computing as a dual-use technology. Once stabilized, they expect it to help financial institutions optimize massive asset portfolios, refine complex risk-pricing models, improve real-time compliance monitoring, and accelerate machine learning used to detect sophisticated fraud networks. They advised firms and national authorities to audit where vulnerable legacy encryption is deployed and keep pace with developments in both quantum technology and generative artificial intelligence.

One Comment